Clover-X
Loading
Portrait of Aman Varma
All team members

Team portfolio

Aman Varma

Identity & Access Management · Identity Governance · Zero Trust

Cybersecurity professional focused on Identity & Access Management. Hands-on enterprise experience with Microsoft Entra ID: identity lifecycle (JML), access reviews, entitlement management, Conditional Access and PIM. SC-300 certified, completing a Master's in Computer Science with a focus on cybersecurity & IAM.

About

Identity is the new perimeter. I help keep it governed.

I combine experience in Identity & Access Management with IT systems administration. At Daimler Truck I administered identities, groups and access in Microsoft Entra ID, supported Joiner-Mover-Leaver processes, ran access reviews, and designed and tested Conditional Access policies aligned with Zero Trust.

Before that, as an IT Office Manager, I ran Active Directory, on- and offboarding and IT support. I'm drawn to identity governance, authorization concepts, access governance platforms and compliance in regulated environments, and to how AI can improve governance processes.

  • i

    Authenticate

    Strong sign-in by default: MFA, Conditional Access and risk-based policies aligned with Zero Trust.

  • ii

    Authorize

    Least privilege through RBAC, app roles, entitlement management and just-in-time activation with PIM.

  • iii

    Audit

    Access reviews, structured documentation and Graph-based reporting that keep access audit-ready.

Projects

Security, identity & lab work

  • SecuritySoftware2026 – present

    AccessPilot: identity governance platform

    A governance layer over Entra ID, Okta and Active Directory that controls who has access to what, for how long, and under whose approval.

    Personal project

    • Python / FastAPI
    • PostgreSQL
    • React / TypeScript
    • Graph API
    • Okta
    • LDAPS
    • SoD
    • Access Reviews
    Read case study: AccessPilot: identity governance platform

    Problem

    Directories like Entra ID, Okta or Active Directory handle authentication, but none provides an end-to-end request, approval, activation, expiry and review lifecycle across several directories.

    Approach

    FastAPI backend with PostgreSQL and a React/TypeScript frontend. One shared connector interface for Entra ID (Graph API), Okta, Active Directory (LDAPS) and CSV/HR feeds, with a joiner-mover-leaver engine, birthright policies, access packages, business roles, multi-stage workflows, separation of duties, access reviews, an entitlement catalog and audit logging on top.

    Result

    A working IGA platform with HR pull sync, multi-directory provisioning, self-healing background workers and break-glass access, documented in a full architecture reference.
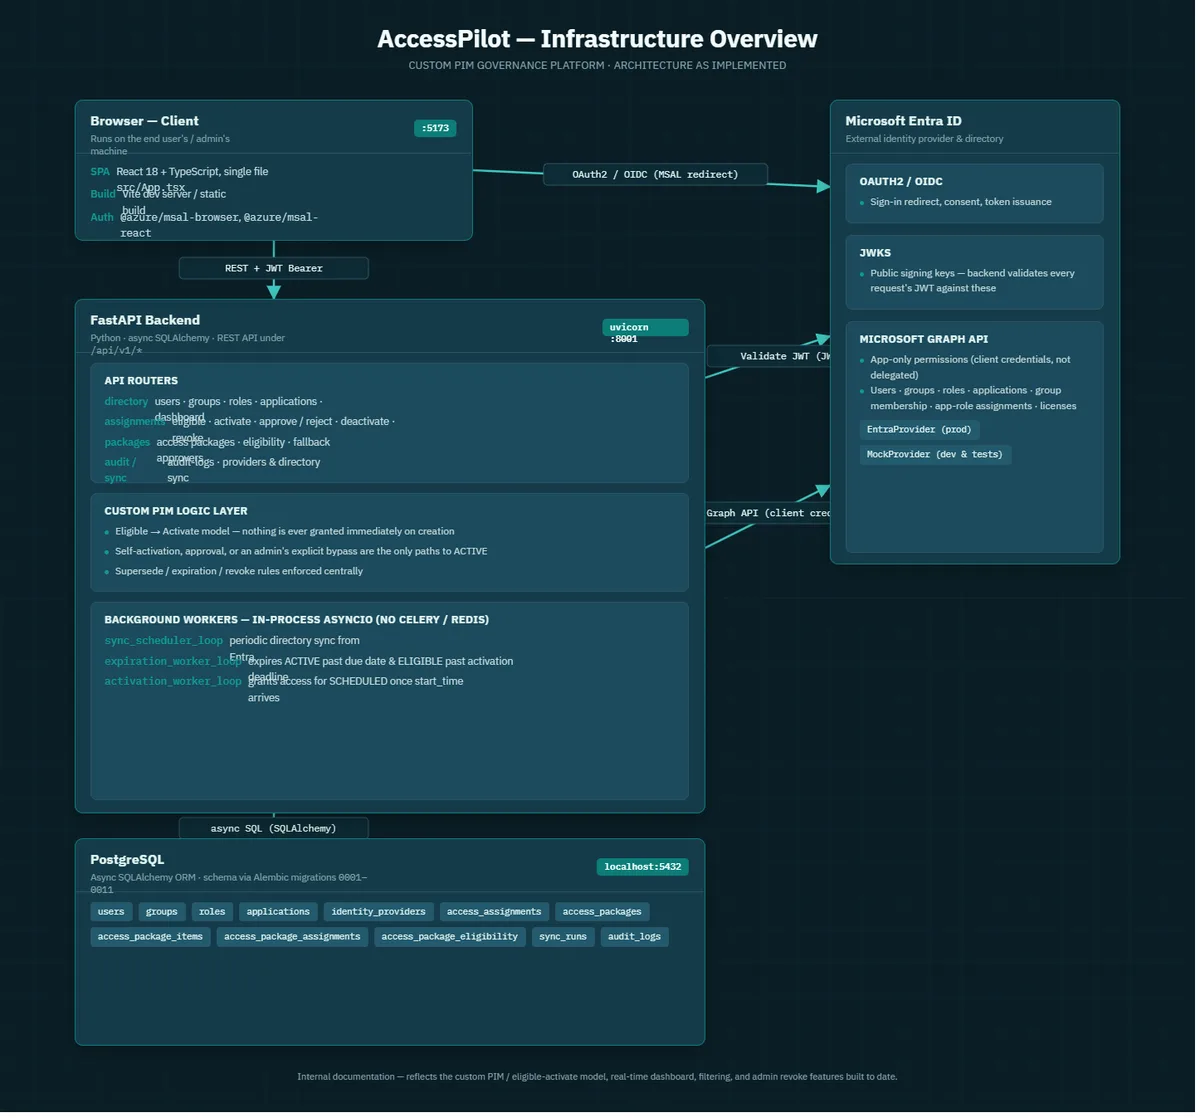
    AccessPilot architecture: React client signs in through Entra ID, calls a FastAPI backend with a custom privileged-access logic layer and background workers, backed by PostgreSQL.
    Infrastructure overview
  • SecurityWeb Apps2025

    PhishIntel Analyzer

    A web app that analyses phishing .eml files using an NLP model, heuristics and threat-intelligence lookups.

    Security project

    • Python
    • Flask
    • NLP
    • Threat Intelligence
    Read case study: PhishIntel Analyzer

    Problem

    Assessing suspicious emails quickly and explainably needs more than a single detection method.

    Approach

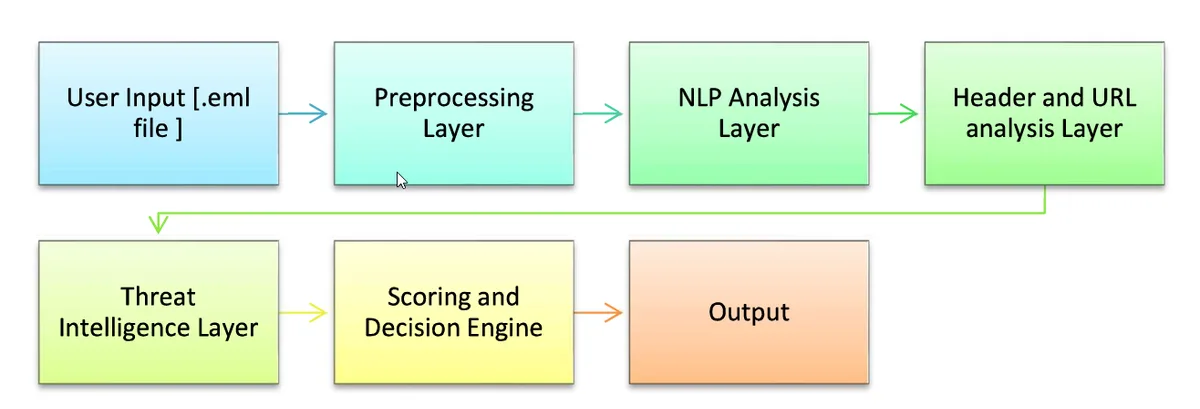
    A Flask app that parses .eml files and combines three methods: a pre-trained NLP model, rule-based heuristics and threat-intelligence integration.

    Result

    Each email is scored using all three methods, documented in an article and a project report.

    PhishIntel pipeline: email input, preprocessing, NLP analysis, header and URL analysis, threat intelligence, scoring and decision engine, output.
    Analysis pipeline
  • SecurityWeb Apps2025

    LogSentinel

    Log analysis platform for small businesses to monitor server and authentication logs and spot suspicious activity.

    Security project

    • Python
    • Flask
    • Log analysis
    Read case study: LogSentinel

    Problem

    Small businesses rarely have the security expertise to make sense of server and authentication logs.

    Approach

    A web-based platform that ingests logs, detects suspicious activity and visualises security-relevant patterns.

    Result

    Security-relevant anomalies become visible without deep cybersecurity know-how.

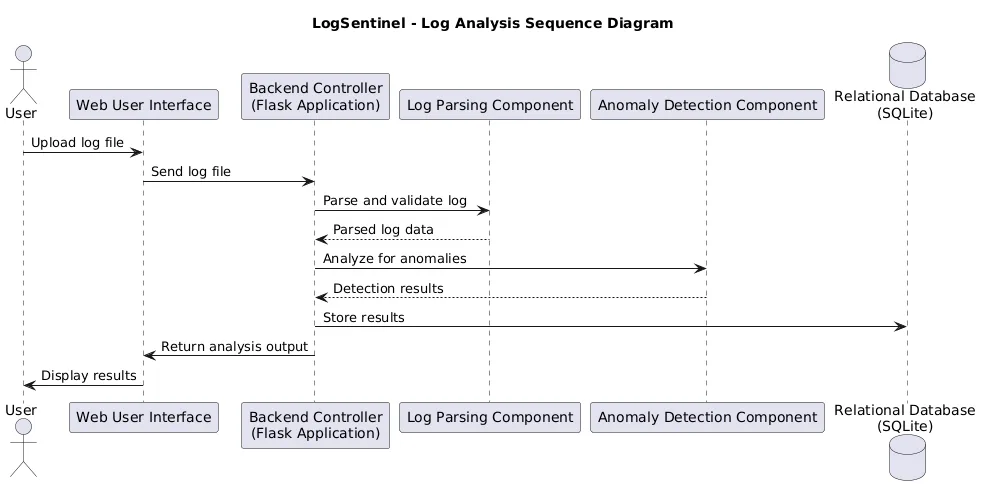
    LogSentinel sequence: the user uploads a log file, the Flask backend parses and validates it, runs anomaly detection, stores results and displays them.
    Log analysis sequence
  • Web AppsSecurityAzure lab

    Secure web app with Entra ID

    Node.js app on Azure App Service with Entra ID authentication (Easy Auth) and RBAC via App Registration.

    Lab project

    • Azure App Service
    • Entra ID
    • Easy Auth
    • Node.js
    • RBAC
    Read case study: Secure web app with Entra ID

    Problem

    A web app had to be reachable only by explicitly assigned users, without writing custom login code.

    Approach

    Deployed to Azure App Service, authentication through Entra ID (Easy Auth), App Registration and an Enterprise Application with user assignment required.

    Result

    Access limited to assigned users, documented as a step-by-step article.

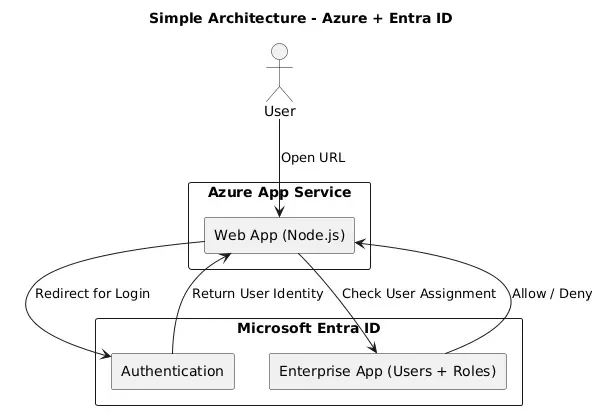
    Architecture: the user opens the web app on Azure App Service, which redirects to Entra ID for sign-in and checks the user's assignment before allowing access.
    Simple architecture: Azure + Entra ID

Experience

Experience & education

  1. Cybersecurity Intern, Identity & Access Management

    Mar 2026 – Sep 2026

    Daimler Truck · Stuttgart

    • Administered identities, groups and access in Microsoft Entra ID; supported JML processes, access reviews and entitlement management.
    • Designed and tested Conditional Access policies aligned with Zero Trust; supported Identity Protection and PIM; managed enterprise apps, SSO and B2B.
    • Automated IAM reporting with Graph API and PowerShell, built Power BI dashboards and presented findings to stakeholders.
  2. Digital Forensic Intern

    Jun 2024 – Aug 2024

    IIMT College of Engineering · India

    • Supported IT security incident identification and vulnerability analysis.
    • Supported ISO/IEC 27001-related compliance and audit documentation.
  3. IT Office Manager

    Jun 2022 – Mar 2024

    Prime Machinery · India

    • Managed Active Directory: user accounts, groups, permissions and password policies.
    • Ran onboarding and offboarding, including account creation, access provisioning and access removal.
    • Provided L1/L2 IT support through a structured ticketing workflow; maintained IT documentation and asset records.
  4. Master of Computer Science (Cybersecurity, IAM focus)

    2024 – 2027

    IU International University of Applied Sciences · Berlin

  5. Bachelor of Computer Applications (B.C.A.)

    2019 – 2022

    Gujarat University · India

Toolbox

What I work with

Identity platforms

  • Microsoft Entra ID
  • Active Directory
  • Microsoft 365
  • Access Reviews
  • Entitlement Management
  • PIM
  • Identity Protection
  • B2B External Identities
  • SailPoint IIQ / ISC (conceptual)
  • ServiceNow

Protocols & automation

  • SAML
  • OAuth 2.0
  • OpenID Connect
  • MFA
  • Conditional Access
  • Zero Trust
  • RBAC
  • Microsoft Graph API
  • PowerShell
  • Power BI
  • n8n
  • ISO/IEC 27001 (basic)
  • NIST (basic)

Certifications

  • SC-300: Microsoft Identity and Access AdministratorMicrosoft
  • Cybersecurity EssentialsCisco
  • Network DefenseCisco
  • Ethical HackerCisco
  • Cybersecurity FundamentalsIBM
  • IT Fundamentals (ITF+)CompTIA
  • German language test (DTZ): B1g.a.s.t.